Almost every guide to the EU AI Act describes it as one body of law. Since 27 July 2026 it has behaved as three, each with its own start date, and treating them as one is how programmes end up building high-risk documentation while the duties that bite today go unmet.
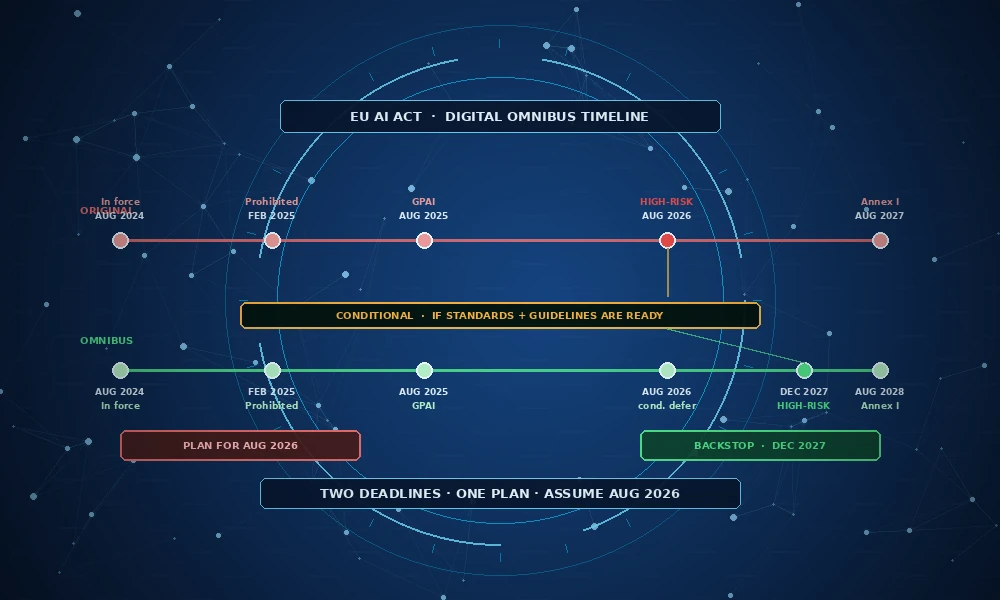
Regulation (EU) 2026/1744, the Digital Omnibus on AI, made 88 modifications to the EU AI Act through 43 numbered amendment points, all effective 27 July 2026. The most consequential was to Article 113. Chapter III Sections 1 to 3, meaning Articles 6 through 27, now apply from 2 December 2027 for Annex III systems and 2 August 2028 for Annex I systems.
Read that carefully, because it reverses the usual advice. EU AI Act provider obligations under Article 16, the Article 9 to 15 requirements, Article 26 deployer duties and the Article 27 impact assessment are enacted law and not yet applicable. What binds today is a different, smaller and widely ignored set.
Scope comes first below, then the duties live now, then December 2027, then August 2028.
Before either date: is it an AI system, and does the Regulation reach you
Two threshold questions decide whether the EU AI Act matters to a given system at all, and both sit before any risk tier.
Is the thing an AI system. The EU AI Act defines one at Article 3(1) as “a machine-based system that is designed to operate with varying levels of autonomy and that may exhibit adaptiveness after deployment, and that, for explicit or implicit objectives, infers, from the input it receives, how to generate outputs such as predictions, content, recommendations, or decisions that can influence physical or virtual environments”. The Omnibus left that definition alone. Inference is the operative word: a deterministic rules engine that applies thresholds a human wrote does not infer, and sits outside. The Commission published guidelines on the definition in February 2025, adopted as C(2025) 5053 final on 29 July 2025, and states in them that they bind nobody and that only the Court of Justice can interpret the Act authoritatively.
Does it reach you. EU AI Act scope under Article 2(1) catches providers placing AI systems on the Union market wherever established, deployers established or located in the Union, and providers and deployers in a third country where the output is used in the Union. A model scoring applications in Bangalore, where the decision lands on a person in Dublin, is inside it. No European entity is needed.
EU AI Act exclusions run narrower than the summaries suggest. Military, defence and national security under Article 2(3). Scientific research and development under Article 2(6). Research, testing and development before market placement under Article 2(8), which closes its own gap: “testing in real world conditions shall not be covered by that exclusion”. Personal non-professional use by a natural person under Article 2(10). Free and open-source licensing under Article 2(12), “unless they are placed on the market or put into service as high-risk AI systems or as an AI system that falls under Article 5 or 50”, which means open licensing removes nothing where the system is high-risk, prohibited or transparency-bound.
Live today: prohibitions, literacy, transparency, incidents and the GPAI chapter
The EU AI Act binds five obligation sets as of 12 September 2026, and none of them depends on a high-risk classification.
Article 5 prohibitions, since 2 February 2025. The EU AI Act bans eight practices outright: subliminal or purposefully manipulative techniques that materially distort behaviour and cause significant harm; exploitation of vulnerabilities based on age, disability or a specific social or economic situation; social scoring leading to detrimental treatment in unrelated contexts or disproportionate to the behaviour; individual criminal risk prediction based solely on profiling or personality traits; untargeted scraping of facial images from the internet or CCTV; inference of emotions in workplaces and education institutions, except for medical or safety reasons; biometric categorisation deducing race, political opinions, trade union membership, religious beliefs, sex life or sexual orientation; and real-time remote biometric identification in public for law enforcement. Biometric identification carries the heaviest conditions: Annex II offences punishable by at least four years, prior authorisation by a judicial or independent administrative authority, an urgency route requiring a request within 24 hours, and a completed Article 27 assessment plus registration.
Two further prohibitions arrive on 2 December 2026: non-consensual intimate imagery under new Article 5(1)(ba) and child sexual abuse material under (bb). New Articles 5(1a) and (1b) narrow them, so for a provider the practice is prohibited only where such generation is the intended purpose, or a reasonably foreseeable and reproducible outcome without significant technical modification and the system lacks adequate safeguards.
Article 4 AI literacy, since 2 February 2025. Providers and deployers must take measures to support the development of AI literacy among staff and others operating systems on their behalf. Article 4 sits in Chapter I, refers to no risk tier, and binds every provider and deployer in scope.
Reports that the Omnibus deleted the EU AI Act literacy duty described a November 2025 proposal. The adopted text replaced and softened it. The old duty was to “ensure, to their best extent, a sufficient level” of literacy. The current duty is to “support the development of” it, with an express disclaimer that the obligation “does not require providers or deployers to guarantee any specific level of AI literacy of any individual”. A results duty became a means duty. Article 4 is also absent from the Article 99(3), (4) and (5) fine bands, leaving penalties to Member States under the general Article 99(1) mandate.
Article 50 transparency, since 2 August 2026. The EU AI Act binds Chapter IV by activity rather than by tier. Providers must design systems that interact directly with people so those people know they are dealing with an AI system, unless that is obvious to a reasonably well-informed observer. Providers of systems generating synthetic audio, image, video or text must mark the output machine-readably and detectably. Deployers of emotion recognition and biometric categorisation must inform the people exposed. Deployers producing deepfakes must disclose it, as must publishers of AI-generated text on matters of public interest.
A dated trap sits in new Article 111(4). Providers of generative systems placed on the market before 2 August 2026 have until 2 December 2026 to meet the Article 50(2) marking duty. Legacy systems are not grandfathered indefinitely.
Article 73 incident reporting, since 2 August 2026. The EU AI Act has providers report serious incidents to the market surveillance authority of the Member State where the incident occurred. Three Article 73 deadlines run, and they do not form a severity ladder: 15 days in general, 2 days for a widespread infringement or a serious and irreversible disruption of critical infrastructure, and 10 days where a person dies. Teams that assume death carries the shortest clock build the wrong escalation path.
Chapter V general-purpose AI, since 2 August 2025. The EU AI Act classifies a model at Article 51 as carrying systemic risk where cumulative training compute exceeds 10 to the power of 25 floating point operations, a lower bar than the 10 to the power of 26 California chose in SB 53. Article 53 requires technical documentation, information for downstream providers, a copyright policy and a sufficiently detailed public summary of training content. Article 55 adds model evaluation with adversarial testing, systemic risk mitigation, incident reporting to the AI Office and cybersecurity protection, and the Code of Practice is the route most providers use to show compliance.
The open-source exemption here runs narrower than its reputation. Article 53(2) removes the documentation duties at 53(1)(a) and (b) for models under a free and open-source licence permitting access, use, modification and distribution, whose parameters including weights, architecture and usage information are public. The copyright policy and the public training-content summary stay fully in force, and the exemption disappears entirely for systemic-risk models. Releasing weights under a restrictive licence qualifies for nothing.
Models placed on the market before 2 August 2025 have until 2 August 2027 to reach compliance, under Article 111(3).
Starting 2 December 2027: the Annex III high-risk regime
Everything in this section is EU AI Act law that applies to nobody yet. Fifteen months is the planning window, not a reason to defer, because the artefacts take longer to build than the time remaining.
Role decides the duty set, and most organisations misread it. A provider under Article 3(3) develops an AI system and places it on the market or puts it into service under its own name. Provider is an EU AI Act definition, not a commercial description. Article 3(11) defines putting into service to include supply “for own use in the Union for its intended purpose”. A bank building its own credit model and running it internally is a provider. No sale happens and provider duties attach anyway. Most such organisations are also deployers under Article 3(4), so they hold both sets.
The EU AI Act flips buyers into providers under Article 25, on three triggers. Putting your name or trademark on a high-risk system already on the market. Substantially modifying one so it remains high-risk. Or modifying the intended purpose of a system, including a general-purpose AI system, so that it becomes high-risk. The third is the live one: repointing a general model at CV screening makes the organisation that did it the provider.
Amended Article 25(2) then provides that the initial provider stops being the provider and must hand over technical documentation sufficient to assess Article 16 compliance, known limitations and failure modes, and targeted technical access for testing. And then the clause procurement teams should read twice: that duty does not apply “in cases where the initial provider has clearly specified that its AI system is not to be changed into a high-risk AI system”. A vendor can disclaim it in its documentation, leaving a buyer with provider obligations and no right to the material. New Article 99(4)(da) brings breaches of Article 25(2) and (4) into the 3 percent penalty band for the first time.
Article 16 is what a provider actually owes. Twelve EU AI Act points, unamended by the Omnibus: ensure compliance with the Section 2 requirements; put identifying details on the system or its documentation; operate a quality management system under Article 17; keep the Article 18 documentation; keep logs under Article 19 where under their control; complete conformity assessment under Article 43 before market placement; draw up the EU declaration of conformity under Article 47; affix the CE marking under Article 48; register under Article 49(1); take corrective action under Article 20; demonstrate conformity on reasoned request from a national authority; and meet accessibility requirements under the Web Accessibility and European Accessibility Directives.
Articles 9 to 15 are the requirements those obligations point at. A risk management system run as a continuous iterative process across the lifecycle comes from Article 9. Article 10 sets data governance and quality criteria for training, validation and testing sets, including bias examination and mitigation. Article 11 requires technical documentation containing at least the Annex IV elements. Article 12 requires automatic logging over the system’s lifetime. Article 13 requires transparency sufficient for deployers to interpret output, with instructions for use. Article 14 requires human oversight design, including override and stop capability and awareness of automation bias. Article 15 requires accuracy, robustness and cybersecurity, with declared accuracy levels and resilience to data poisoning, model poisoning, adversarial examples and confidentiality attacks.
Only Articles 10 and 11 were touched here. Article 10(5) was deleted and relocated into a new Article 4a covering the processing of special categories of personal data for bias detection and correction, now extended beyond high-risk systems and carrying an explicit rider that it “does not create any obligation to conduct such bias detection and correction”. Article 11(1) gained a genuine concession: SMEs, start-ups and small mid-caps may supply the Annex IV elements “in a simplified manner” on a Commission form, and notified bodies shall accept that form. Article 17(2) was replaced in the same spirit, making the quality management system proportionate to organisation size.
Conformity assessment is lighter than most budgets assume. Article 43(2) is explicit: for Annex III points 2 to 8, covering education, employment, essential services, law enforcement, migration and justice, providers follow internal control under Annex VI, “which does not provide for the involvement of a notified body”. Only Annex III point 1, biometrics, offers the notified body route under Annex VII, and even there a notified body becomes mandatory only where harmonised standards or common specifications are absent or unapplied. Harmonised standards supporting EU AI Act conformity remain in development at CEN-CENELEC JTC 21, which is why most technical files are being written against the articles themselves.
The EU AI Act gives deployers twelve paragraphs at Article 26. Technical and organisational measures to use the system per its instructions. Human oversight assigned to people with “the necessary competence, training and authority, as well as the necessary support”. Input data relevant and sufficiently representative where the deployer controls it. Monitoring, with a duty to suspend use and inform the authority where an Article 79(1) risk appears. Log retention “for a period appropriate to the intended purpose of the high-risk AI system, of at least six months”, which is a floor under a purpose test rather than a fixed term. Registration duties for public authorities. Use of Article 13 information to support a GDPR data protection impact assessment. Rules for post-remote biometric identification, including authorisation within 48 hours. A duty to inform workers’ representatives and affected workers before putting a system into use at the workplace. A duty to inform natural persons subject to decisions made or assisted by an Annex III system. And cooperation with competent authorities.
The Article 27 assessment binds a narrower group than guidance claims. Bodies governed by public law and private entities providing public services owe a fundamental rights impact assessment for Annex III systems other than critical infrastructure. Beyond them, any deployer at all owes one for Annex III point 5(b), creditworthiness evaluation and credit scoring, and point 5(c), risk assessment and pricing in life and health insurance. A private lender or insurer is inside it on the strength of the use case alone. Amended Article 27(4) now allows cross-references to a GDPR Article 35 assessment instead of duplicating the work, and amended 27(5) tasks the AI Office with a questionnaire template, including through an automated tool.
Starting 2 August 2028: the Annex I product regime, now narrower
Annex I of the EU AI Act covers artificial intelligence used as a safety component of a product, or as a product, under sectoral harmonisation legislation requiring third-party conformity assessment. Annex I duties arrive eight months after the Annex III set.
The Omnibus narrowed that gateway materially. New Article 6(1a) provides that systems “solely used for non-safety related aspects of user assistance, performance optimisation, service efficiency, automation or convenience or quality control shall not qualify as safety components”. Article 6(1b) pulls back anything whose failure would endanger health and safety. Article 6(1c) removes products needing third-party assessment only for reasons unrelated to health and safety, such as radio spectrum interference. A predictive maintenance model on a production line now sits outside unless its failure could hurt someone.
Amended Article 43(3) also confirms that manufacturers “are not required to choose a conformity assessment procedure involving third-party conformity assessment only because the product includes a high-risk AI system as a safety component”, where the sectoral legislation does not require it. Notified bodies already designated under Annex I Section A legislation must apply for designation under the Act by 28 January 2028.
The escape route that survived: Article 6(3)
Article 6(3) was left untouched and remains the most useful provision the EU AI Act offers. An Annex III system is not high-risk where it poses no significant risk of harm, and any one of four conditions carries it: a narrow procedural task, improving the result of a previously completed human activity, detecting decision-making patterns without replacing human assessment, or performing a preparatory task.
One EU AI Act sentence closes the door: “an AI system referred to in Annex III shall always be considered to be high-risk where the AI system performs profiling of natural persons.”
Claiming the derogation costs paperwork rather than nothing. Documentation is required by Article 6(4) the assessment to be documented before the system goes to market or into service, and Article 49(2) registration still applies. The AI Act Service Desk is the official route for classification questions.
Every operative date, in one place
| Date | What applies |
| 2 Feb 2025 | Chapter I including Article 4 literacy; Article 5 prohibitions (a) to (h) |
| 2 Aug 2025 | Chapter V GPAI; governance; notified bodies; penalties except Article 101 |
| 27 Jul 2026 | Regulation (EU) 2026/1744 in force; all 88 modifications effective |
| 2 Aug 2026 | General application: Article 50, Article 43, Article 73, Article 101 |
| 2 Dec 2026 | New NCII and CSAM prohibitions; Article 111(4) legacy generator deadline |
| 2 Aug 2027 | Article 111(3): GPAI models placed before 2 Aug 2025 must comply |
| 2 Dec 2027 | Chapter III Sections 1 to 3 for Annex III high-risk systems |
| 28 Jan 2028 | Notified bodies under Annex I Section A must apply for designation |
| 2 Aug 2028 | Chapter III Sections 1 to 3 for Annex I high-risk systems |
| 2 Aug 2030 | Backstop for high-risk systems intended for use by public authorities |
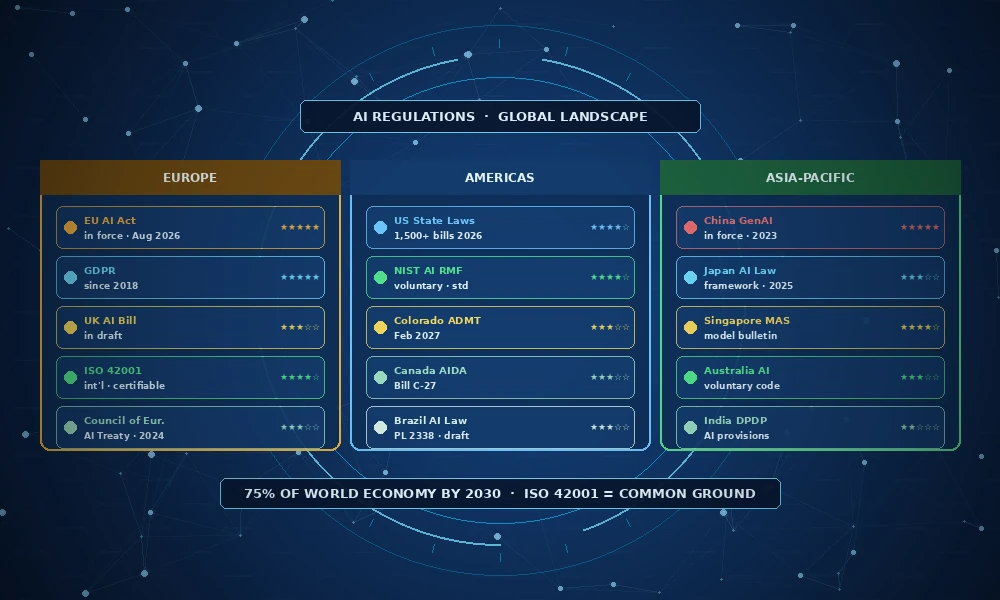
EU AI Act guidance still giving 2 August 2026 as the high-risk deadline predates the amendment. A single December 2027 date understates the Annex I position by eight months. Every date that shifted is traced in the change ledger, and how these figures compare with other jurisdictions sits in the global regulation tracker.
One further provision is worth a line of its own. The Article 111(2) grandfathering hook now floats: high-risk systems already on the market before the Chapter III application date are caught only if they undergo significant design changes after it, and the reference is no longer a fixed 2 August 2026.
Penalties, and the band that actually applies to you
Three penalty bands sit in the EU AI Act. Article 99(3) sets EUR 35 million or 7 percent of worldwide annual turnover, whichever is higher, for the Article 5 prohibitions. Article 99(4) sets EUR 15 million or 3 percent for the operative duties of providers, deployers, importers, distributors and notified bodies, and for Article 50. Article 99(5) sets EUR 7.5 million or 1 percent for supplying incorrect or misleading information. Article 101 sits outside this scheme, letting the Commission fine general-purpose model providers directly at 3 percent or EUR 15 million.
Most exposure lands in that middle band, and for smaller companies the arithmetic reverses. Article 99(6) gives SMEs and start-ups the percentage or the fixed amount, whichever is lower, and new paragraph 6a extends that to small mid-caps for the 99(4) and 99(5) bands. New Article 3 definitions (14a) and (14b) are what make both concessions operable.
One quiet addition signals where enforcement is heading. New Annex XIV of the EU AI Act sets notified body designation codes, and code AIH 0401 covers “AI systems based on other emerging AI technologies not covered by other codes, including Agentic AI”.
What the Act asks you to be able to produce
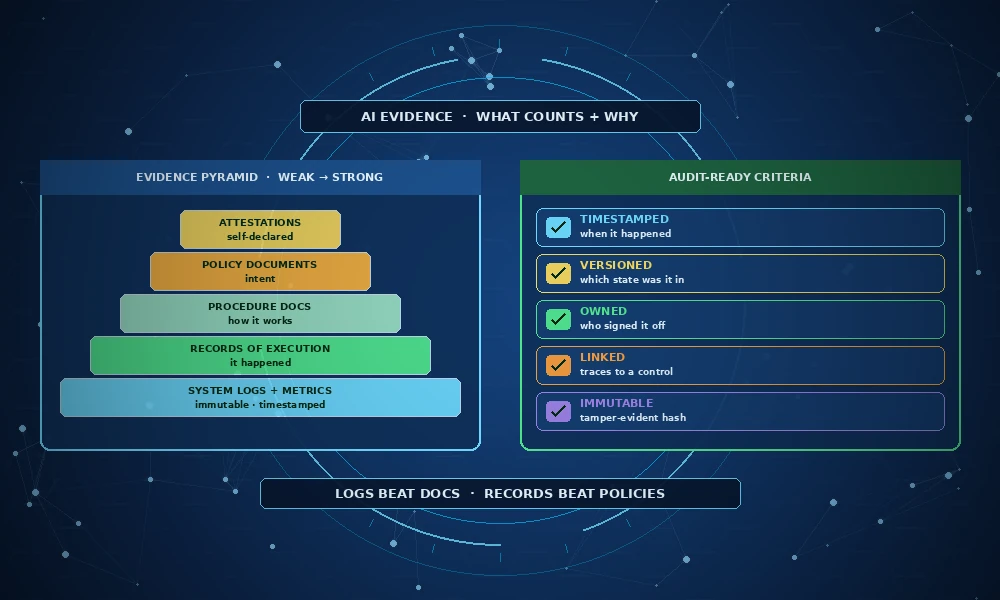
Strip the EU AI Act back and its obligations resolve into records that somebody has to hold. Technical documentation under Annex IV. A quality management system under Article 17. Logs under Articles 19 and 26(6). Conformity assessment and the declaration under Article 47. Registration under Article 49. Post-market monitoring under Article 72. Serious incident reports under Article 73. Human oversight evidence under Article 14. The Article 6(3) assessment where the derogation is claimed. The Article 27 assessment where it binds.
Ten artefact families come out of the EU AI Act, each with an owner, a retention clock and a trigger. Which record answers which article is worked out in the records that prove conformity, and the mapping between these duties and the ISO/IEC 42001 and NIST AI RMF control sets is in where these instruments overlap.
Where these records are held
Splitting the EU AI Act into three regimes is a scheduling problem before it is a legal one. Duties live today need evidence today. Duties live in December 2027 need a build plan that starts well before it.
Govern365 was built around that distinction. The AI System Registry records each system once with its role, intended purpose, tier and the Article 6(3) reasoning where claimed, so a repurposing decision surfaces the Article 25 consequence before it happens. The Audit Evidence Manager attaches each Annex IV element, log set and assessment to the article it satisfies, with dates and approvers. Governance Workflows carry the human oversight and approval steps Articles 14 and 26 both demand. Continuous Monitoring holds the post-market and incident clocks, including the 15, 10 and 2 day Article 73 deadlines. The platform sits at govern365.ai, and the route from intake to an approved, evidenced system is shown on where these approvals are tracked.
Frequently asked questions
Which EU AI Act obligations apply right now?
Article 5 prohibitions and Article 4 AI literacy, both since 2 February 2025. Chapter V general-purpose AI rules since 2 August 2025. Article 50 transparency, Article 43 conformity assessment and Article 73 incident reporting all since 2 August 2026. The high-risk requirements in Articles 9 to 27 are not yet applicable.
When do the high-risk obligations actually start?
The EU AI Act now carries two dates: 2 December 2027 for Annex III systems classified under Article 6(2), and 2 August 2028 for Annex I systems classified under Article 6(1). Regulation (EU) 2026/1744 replaced the former 2 August 2026 date on 27 July 2026.
Does the EU AI Act apply to a company outside the EU?
Yes. The EU AI Act reaches outward through three hooks in Article 2(1). Placing an AI system on the Union market catches a provider wherever established. Being established or located in the Union catches a deployer. Producing output used in the Union catches providers and deployers in third countries.
Are we a provider or a deployer if we built the system ourselves?
Both, usually. The EU AI Act makes you a provider under Article 3(3) where you put a system into service under your own name, and Article 3(11) defines putting into service to include supply for your own use. Building internally and running it yourself attracts provider duties without any sale.
Does a high-risk AI system need an external audit?
Usually not. The EU AI Act requires internal control under Article 43(2) under Annex VI for Annex III points 2 to 8, covering education, employment, essential services, law enforcement, migration and justice, and states that it “does not provide for the involvement of a notified body”. Only Annex III point 1 biometric systems can take the notified body route.
How fast must a serious incident be reported?
Within 15 days generally, within 2 days for a widespread infringement or a serious and irreversible disruption of critical infrastructure, and within 10 days where a person dies. The death deadline is longer than the critical infrastructure one, which catches teams expecting a severity ladder.
Does the open-source exemption cover general-purpose AI models?
Partly. Article 53(2) removes the technical documentation and downstream information duties for models under a free and open-source licence with public weights, architecture and usage information. The copyright policy and the public training-content summary still apply, and the exemption does not apply at all to models with systemic risk.